

ISO/IEC 25000:2014 Certification Services
ISO/IEC 25000:2014 establishes a framework supporting the specification and evaluation of quality requirements for systems and software products, providing common reference models, definitions, and relationships among the standards, superseding the earlier ISO/IEC 9126 and ISO/IEC 14598 standards.
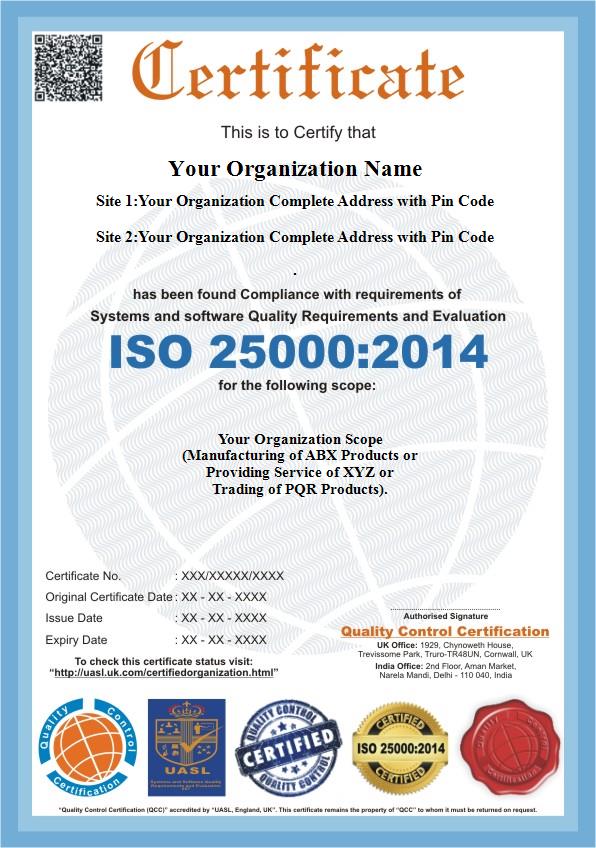
Certification to ISO/IEC 25000:2014 supports organizations in establishing a structured approach to management and demonstrating conformity through an objective assessment process.
What is ISO/IEC 25000:2014?
ISO/IEC 25000:2014 is an internationally recognized standard published by the International Organization for Standardization (ISO). It specifies requirements for establishing, implementing, maintaining, and continually improving a software quality requirements & evaluation (square).
ISO/IEC 25000:2014— Current Version
ISO/IEC 25000:2014 is the current edition of the standard. It incorporates a risk-based approach and follows the shared ISO high-level structure, placing greater emphasis on the role of leadership, organizational context, and alignment with strategic direction.
Key aspects of ISO/IEC 25000:2014 include:
- Consideration of risks and opportunities within processes
- Greater involvement of top management
- Alignment of objectives with organizational context
- Flexible documented information requirements
Importance of ISO/IEC 25000:2014 Certification
ISO/IEC 25000:2014 certification demonstrates that an organization's software quality requirements & evaluation (square) has been independently evaluated and found to conform to the requirements of the standard. It is widely recognized across industries and sectors.
- Provides independent assurance of conformity to software quality requirements & evaluation (square) requirements
- Supports participation in tenders and contractual requirements
- Enhances consistency in organizational processes
- Strengthens credibility with interested parties
- Facilitates alignment with internationally accepted practices
Certification Process
The certification process is conducted in accordance with applicable standards and established audit principles, ensuring impartiality, consistency, and transparency.
Step 1 — Inquiry and Application Submission
The process is initiated upon receipt of an inquiry and a completed application form, providing details of the organization's activities, scope, and relevant information.
Step 2 — Application Review and Confirmation
The application is reviewed to determine the scope of certification, audit requirements, and necessary arrangements for the certification process.
Step 3 — Stage 1 Audit Planning
An audit plan for Stage 1 is prepared and communicated, defining the scope, objectives, and schedule of the audit.
Step 4 — Stage 1 Audit Conduct
A Stage 1 audit is conducted to evaluate management system documentation, assess site-specific conditions, and determine readiness for Stage 2.
Step 5 — Stage 2 Audit Planning
Following Stage 1, a detailed audit plan for Stage 2 is established for the evaluation of system implementation and effectiveness.
Step 6 — Stage 2 Audit Conduct
A Stage 2 audit is conducted to assess conformity of the management system with the applicable standard requirements.
Step 7 — Certification Decision and Issue of Certificate
An independent review of audit findings is carried out prior to the certification decision. Upon a positive certification decision, the certificate is issued.
Benefits of ISO/IEC 25000:2014
- Improved consistency of products and services
- Enhanced customer satisfaction
- Structured and controlled processes
- Objective measurement and monitoring of performance
- Continual improvement of the management system
Frequently Asked Questions
1. What does ISO/IEC 25000:2014 certification represent?
It confirms that an organization's management system has been assessed and found to conform to ISO/IEC 25000:2014 requirements.
2. What is ISO/IEC 25000:2014?
It is the current version of the software quality requirements & evaluation (square) standard, incorporating risk-based thinking and enhanced leadership involvement.
3. How is certification granted?
Certification is granted following successful completion of Stage 1 and Stage 2 audits and an independent certification decision process.
4. Is certification applicable to all organizations?
Yes, ISO/IEC 25000:2014 is applicable to organizations of all sizes and sectors.
Why QCC Certification
- Impartial and independent certification activities
- Structured audit methodology in line with applicable standards
- Competent and qualified audit personnel
- Consistent and transparent certification process
- Adherence to applicable accreditation and regulatory requirements
Contact
For further information regarding ISO/IEC 25000:2014 certification, please contact our office.